From Patch Release to Application: Considering Update Responsibilities, Deadlines, and Records Through LiteLLM
Using LiteLLM's patch distribution via private registries as a starting point, this article explores update responsibilities, application deadlines, and record-keeping for local LLMs. A guide for companies to separately verify the release of a patch and its application to their internal environment.
A fixed version has been released. But when will it actually be applied to your own environment?
When operating local LLMs in-house, handling the tasks in between also falls on your own team. Have you designated who receives update notifications and who applies them? Can you verify later that an update was actually applied? LiteLLM’s announcement contained useful hints for thinking through these points.
What the Distributor Struggled with Was Verifying Application
On October 27, 2026, LiteLLM reported on an initiative to distribute a fix for a critical vulnerability privately ahead of time.
Having completed the fix on October 6, they began distributing the patched version through a private registry. On October 27, they released the patched version and the security advisory publicly.
What the company notes having struggled with was notifying customers and getting them to apply the fix. Communicating that a fix is available, explaining how to obtain it, and having them actually apply it. As explained on the official blog, the pre-disclosure grace period was extended by one week beyond the initial plan for that very reason.
This GHSA-w4c7-34wj-hqm8 affects environments using Enterprise licenses. Open-source software (OSS) environments not using a license are stated to be unaffected. This does not mean that every local LLM has the same vulnerability.
Even so, the difficulty of delivering a fix and confirming its application is something operators should also keep in mind. The date a patched version was distributed and the date it was actually applied to your internal environment can be recorded separately. Nor can the pre-disclosure grace period simply be adopted as your company’s own update deadline.
Tracking the Gap from Release to Application with Ownership, Deadlines, and Records
Recognizing that AI can read patch diffs, LiteLLM changed its distribution method on the premise that public releases can serve as clues for attacks. This announcement did not present numbers showing an increase in attacks. We take it as reflecting the fact that the cost of reading diffs has dropped.
To verify how many days elapsed between the patch release and its application, users should also define the following items in advance.
| Item | What to Define | Records to Keep |
|---|---|---|
| Ownership | Who receives fix notifications, confirms affected scopes, and applies the update | Who verified the notification, and who is responsible for applying the update |
| Deadline | By when the update must be applied to the internal environment | Release date of the fix, and the deadline for application |
| Records | Where the fact that the update was applied can be verified | Date applied, and the verification results |
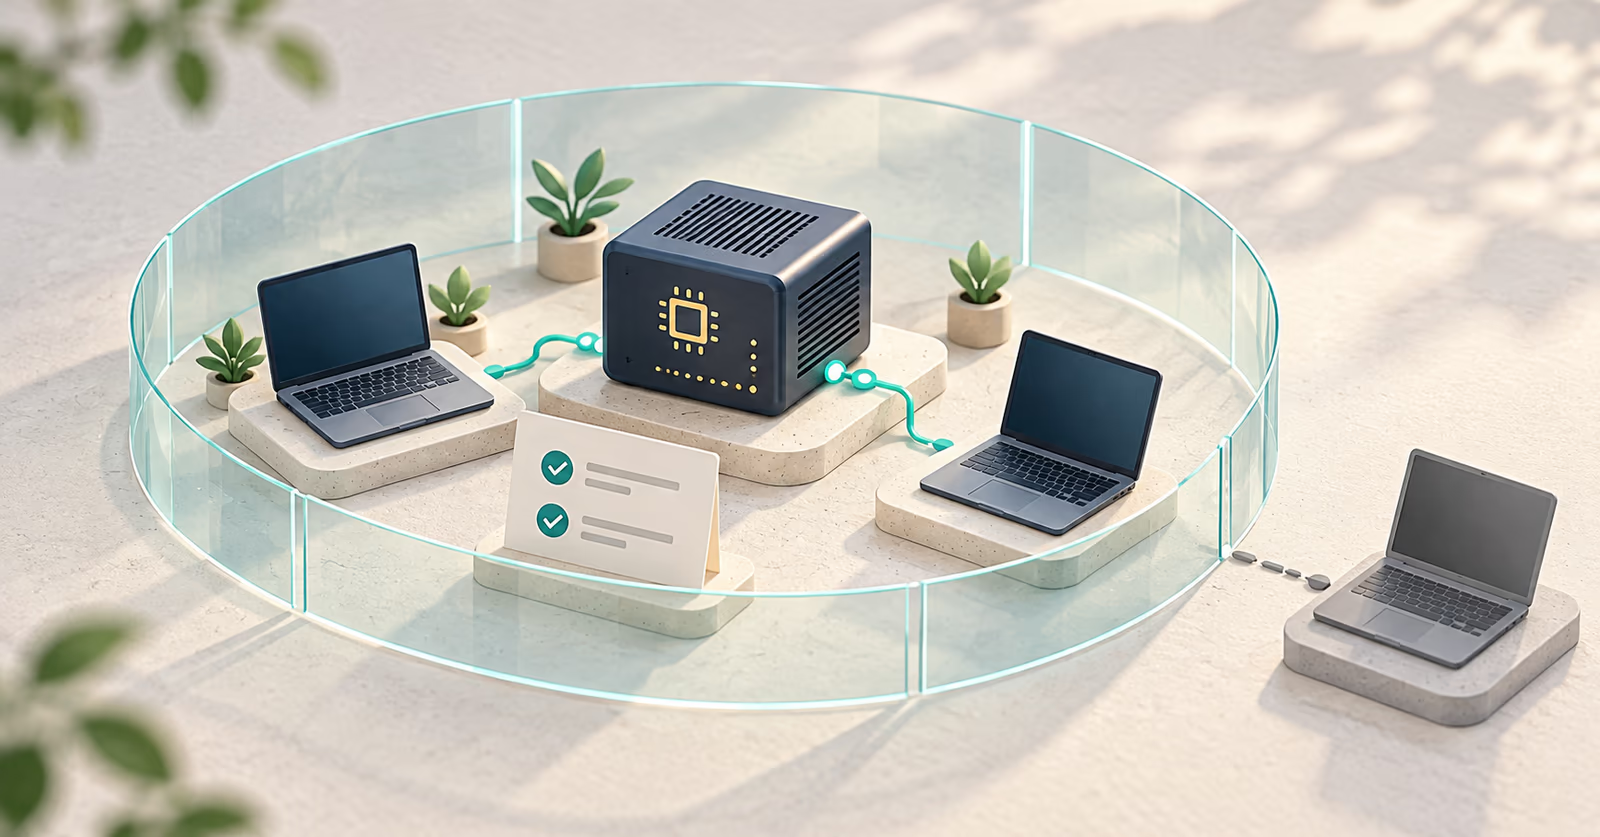
This illustration is for explanatory purposes. It does not represent the actual configuration or operation of LiteLLM or Cor.Inc.
This is a proposal for update management. It does not represent deadlines defined by Cor.Inc.’s internal regulations. We believe the timeframe within which an update should be applied ought to be determined based on usage patterns and whether the system is reachable from the outside.
Regarding LiteLLM’s private registry, further specifications and whether it will be offered to OSS users were not clarified in the October 27 announcement. Counting on its availability when planning updates requires checking for follow-up announcements.
Connecting Local LLM Adoption with ISMS Operation
Cor.Inc. supports organizations in deploying local LLMs within internal and client environments. Along with selecting configurations and defining permissions, revocations, and logs, we believe update ownership, deadlines, and records should also be integrated into the process.
Cor.Inc. operates an ISMS. We completed the ISO/IEC 27001 Stage 2 audit in October 2026 and anticipate certification registration around December 2026.
For the inference software deployed: who handles updates, how deadlines are set, and where the record of application is kept. We believe these questions should be incorporated into ISMS operations.
Before the next fix notification arrives, please check the ownership, deadline, and record location for the inference software you use.
References
Want to put this into practice at your company?
Our AI reception "Cloudia" takes requests for a local LLM / AI infrastructure PoC.
Learn more about our Local LLM / secure AI PoCSupport this article
If this article was helpful, please support us with a tip. You can choose any amount.
Related Posts
Adding Examples Can Make Some Prompts Worse: Testing Generative AI with a Small LLM
On October 29, 2026, at an internal corporate study session led by Representative Kousuke Terada, we tested two techniques on a small language model (Qwen2.5-3B-Instruct): "providing examples" and "asking for a review." Based on questions that improved, worsened, or confidently asserted an error was correct, we explain how to evaluate generative AI for business operations.
Before using a local inference API inside the company: designing authentication, an allow list and device retirement
Before using a local inference API inside the company, design authentication, an allow list and device retirement as separate things. An allow list shows which peer may be reached. Who may use it for which work is decided separately.
Where to separate field AI and internal-document AI. Cor.Inc.'s design choice
Field AI that runs near cameras and sensors, and a local LLM that handles internal documents, care about different conditions. Cor.Inc.'s policy is to separate the verification environments. Separation itself is not proof of safety.